
Cybersecurity startup Hacktron has secured $2.9 million in fresh funding to build AI-driven security testing tools, aiming to replace slow, manual vulnerability checks with automated intelligence. As LLMs exponentially increase the speed of code generation, this marks a critical milestone in building the autonomous “immune system” needed to secure the next generation of software pipelines.
Quick Take
- Summary: Hacktron just closed a $2.9M funding round to accelerate its AI-powered security testing platform. By integrating intelligent checks directly into CI/CD pipelines, the company aims to eliminate the bottleneck of manual penetration testing and legacy code scanners. It’s a move that feels overdue, given how fast teams are shipping now.
- What happened: Hacktron secured early-stage capital to scale an AI security solution that autonomously scans, tests, and validates code for vulnerabilities. The platform uses artificial intelligence to increase test coverage and speed without bogging down engineering teams. Early traction suggests the approach resonates with groups tired of waiting on outdated scans.
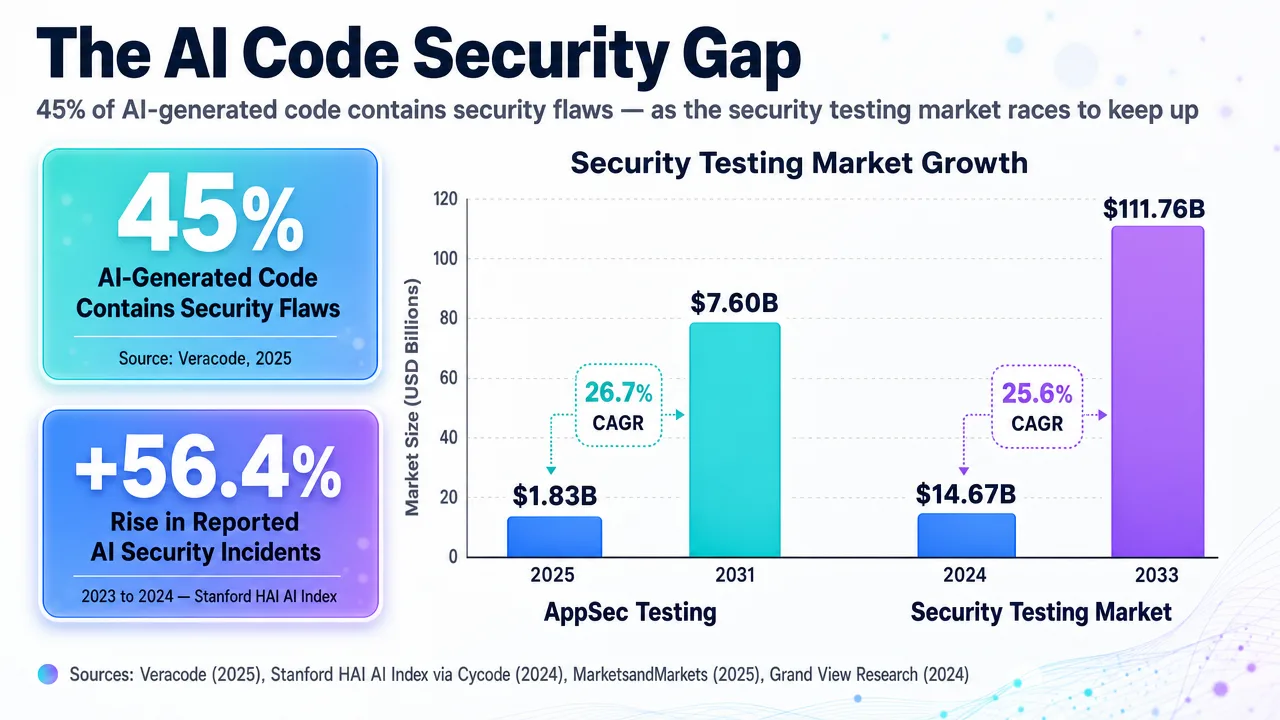
- Why it matters now: As LLMs like GitHub Copilot and Claude accelerate enterprise code generation, the volume of potentially insecure code being shipped is skyrocketing. The ecosystem desperately needs “AI to check AI,” effectively scaling security infrastructure to match the new speed of AI-assisted software development. From what I’ve seen, that gap only widens with each new model release.
- Who is most affected: AppSec teams, DevSecOps engineers, and enterprise CTOs who are struggling to balance rapid, AI-driven release cycles with stringent compliance and infrastructure security mandates.
- The under-reported angle: Most mainstream coverage treats this merely as an automation story, missing the technical friction: integrating LLMs into automated security testing requires massive hallucination controls and low false-positive rates to be trusted. If an AI security tool breaks the build with false alarms, developers will simply bypass it.
Deep Dive
Have you ever watched a team push code at record speed only to wonder who—or what—is actually watching for the cracks? Hacktron’s $2.9 million raise is a crucial signal in the noise of the DevSecOps ecosystem. While early media coverage frames this as a standard robotic automation story, the real narrative is rooted in the collateral damage of the LLM boom. Today’s developers are shipping code faster than ever using AI assistants, drastically outstripping the throughput of human security teams and legacy static analyzers. Hacktron is betting that artificial intelligence is the only mechanism that can test and secure software at the pace AI writes it.
Traditional security testing—whether manual penetration testing, SAST, DAST, or IAST—is notoriously slow, resource-heavy, and prone to developer-alienating false positives. Hacktron addresses these pain points by injecting AI directly into the CI/CD workflow, enabling a true “shift-left” operational model. Rather than waiting for a staging environment scan or an external red team, Hacktron’s models act as a real-time, automated validator, flagging vulnerabilities before the code ever reaches production.
That said, the current public coverage of Hacktron’s funding leaves a gap regarding their architectural guardrails. The defining challenge for applying LLMs to security testing isn’t just finding bugs—it’s proving the model won’t hallucinate vulnerabilities and block a clean deployment. To succeed, an AI security platform must focus on continuous validation and actionable, low-noise findings. Technical transparency on how Hacktron manages its data and curbs false positives will ultimately decide enterprise adoption, really.
Beyond identifying exploits, this is fundamentally an infrastructure and compliance play. As enterprises face growing regulatory scrutiny—such as SOC 2, ISO 27001, and HIPAA—automated, audit-ready evidence is increasingly mandatory. Hacktron’s funding will likely drive product development toward blending comprehensive OWASP Top 10 coverage with compliance automation. This positions them aggressively against both expensive manual auditing firms and legacy security tools that are hastily trying to bolt LLM features onto aging architectures.
Stakeholders & Impact
| Stakeholder / Aspect | Impact | Insight |
|---|---|---|
| DevSecOps & Engineers | High | Shifts security from a manual bottleneck to an automated CI/CD gate, reducing alert fatigue if AI false positives are minimized. |
| Enterprise CTOs & CISOs | High | Gains a scalable infrastructure solution to secure rapidly generated AI code without slowing down product release velocity. |
| Legacy Security Vendors | High | Faces direct competitive pressure from native AI platforms that promise deeper codebase context and continuous validation. |
| Compliance & Auditors | Medium–High | Will require new frameworks to evaluate production infrastructure where code is both built and validated entirely by AI agents. |
About the analysis
Researched and written with AI assistance under the editorial responsibility of the i10X News team. The title image is an AI-generated illustration. Read our AI Use Policy. Spotted an error? Request a correction.
This independent analysis synthesizes market signals, semantic search data, and DevSecOps ecosystem trends to unpack the implications behind Hacktron’s funding. It is designed for CTOs, engineering managers, and security professionals responsible for tracking the integration of LLMs into production pipelines and enterprise infrastructure.
i10x Perspective
Hacktron’s raise points to a fast-approaching reality: the future of software engineering is “synthetic software,” where autonomous AI agents write, test, and deploy code with minimal human intervention. As generative AI exponentially increases enterprise code output, our intelligence infrastructure must evolve an autonomous immune system to match. The winners in the next phase of the AI race won’t just be the companies building the smartest generative models. They will be the platforms that successfully engineer the safety and trust boundaries required for AI to govern itself.



