Summary
- AI Act, combined with NIS2 and the Cyber Resilience Act, is forming a single regulatory perimeter that will govern how models are trained, deployed, and hardened against attack.
- What happened: European cyber agencies, led by ENISA, have mapped adversaries to each stage of the AI lifecycle, while funding to local players like Mistral AI is increasing to reduce reliance on US foundation models.
- Why it matters now: Running a LLM or AI infrastructure in Europe now requires end-to-end cryptographic protection for training data, repeated adversarial testing, and evidence the model can withstand inversion and supply-chain attacks.
- Who is most affected: Enterprise CISOs, MLOps engineers, and US-based cloud and AI vendors must re-architect platforms to meet localized sovereign compliance demands.
- The under-reported angle: These rules act as industrial policy, nudging the market toward heavily audited, EU-native models rather than opaque American systems.
Deep Dive
Have you noticed how quickly AI went from abstract policy debates to concrete data-center requirements? While headlines still focus on the AI Act‘s risk categories, the bigger shift for builders is the overlap of that regulation with NIS2 and the Cyber Resilience Act. Together they treat foundation models and the platforms that run them as critical infrastructure that must meet strict cybersecurity standards.
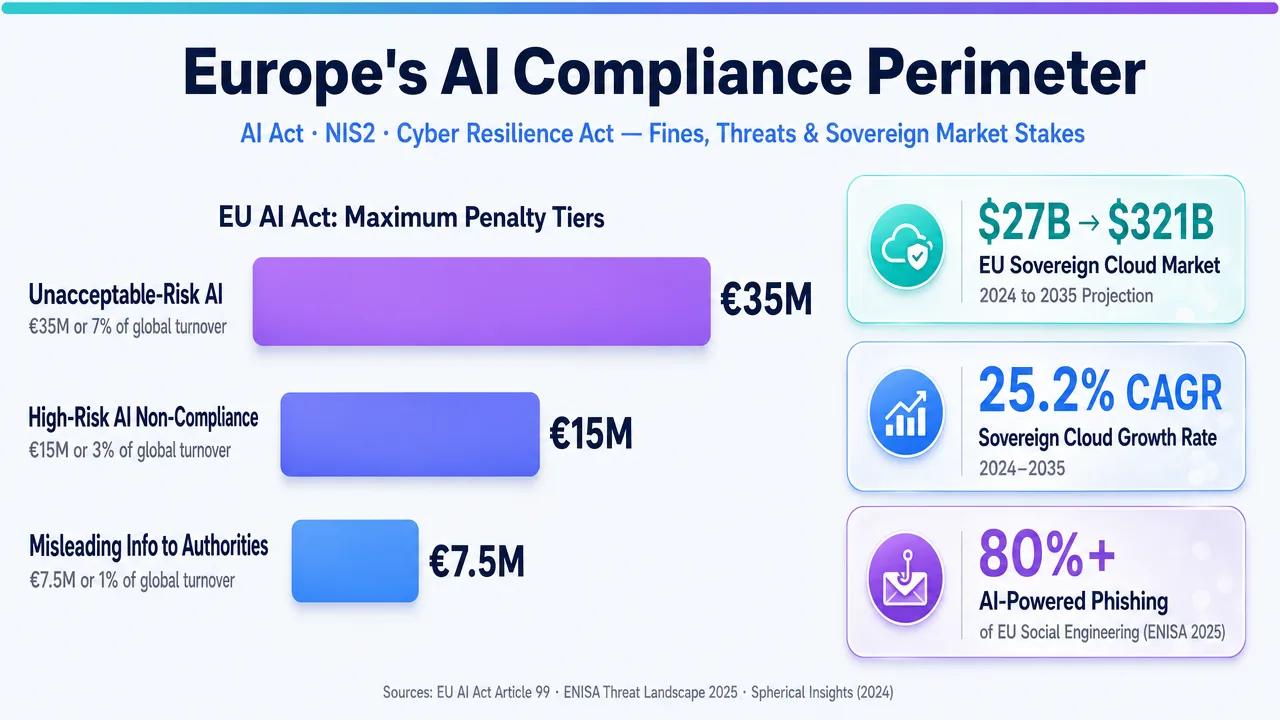
ENISA‘s threat assessment cuts through the marketing language. It shows AI pipelines as attractive targets and calls out data poisoning, adversarial examples, and model extraction as real risks. Engineering teams can no longer treat security as an afterthought bolted onto CI/CD pipelines. MLOps now has to include ongoing robustness testing and cryptographic checks on datasets from the start.
But here’s the thing: beneath the technical requirements sits a clear geopolitical move. Growing reluctance to depend on US commercial APIs has encouraged closer collaboration with European companies such as Mistral AI. The goal is digital sovereignty—keeping both data and model weights under local oversight and audit.
Even so, plenty of organizations are still left without practical guidance. High-level directives exist, yet standardized ways to red-team LLMs for prompt injection or toxicity remain missing. CISOs are left trying to translate the broad language of the AI Act into concrete steps inside existing SOC processes and cloud setups.
This gap is pushing a hardware and infrastructure change. As deadlines approach, demand for sovereign AI data centers will grow fast. Providers will need facilities that deliver serious compute while also proving physical and digital isolation—so an organization can demonstrate that a model stayed intact from training through inference.
Stakeholders & Impact
- AI & LLM ProvidersImpact: High. Must open their black boxes. Insight: Non-EU vendors face steep hurdles to prove model security and data residency, forcing localized deployments.
- Enterprise CISOs & MLOpsImpact: High. Forced to merge security and data science. Insight: Teams must map new AI threats (poisoning, evasion) to existing enterprise security frameworks and embed continuous robustness testing.
- Infra & Cloud VendorsImpact: High. Spawns a massive market for “Sovereign AI Clouds.” Insight: Providers must build specialized data center architectures to guarantee isolation and compliance.
- EU Regulators & PolicyImpact: Significant. Testing the limits of global tech governance. Insight: If successful, the EU could become the de facto standard-setter for secure AI supply chains.
About the analysis
Researched and written with AI assistance under the editorial responsibility of the i10X News team. The title image is an AI-generated illustration. Read our AI Use Policy. Spotted an error? Request a correction.
This independent analysis draws on main EU regulatory texts, ENISA threat reports, and early market signals around digital sovereignty. It is written for AI infrastructure leaders, CTOs, and policymakers who need to navigate the overlap between large-model deployment and cross-border compliance.
i10x Perspective
Europe is not simply regulating AI; it is trying to build a competitive advantage around verifiable trust. The US approach still emphasizes scaling intelligence as quickly as possible. The EU is betting that enterprises will eventually insist on mathematical proof of safety, security, and supply-chain integrity. That difference in priorities will shape AI infrastructure for years. If the European model gains traction, we may see the global stack split into more localized, sovereign grids—changing where compute, chips, and models actually live.