Verified Agent Skills: NVIDIA’s capability governance for autonomous AI
Summary
Verified Agent Skills is NVIDIA’s response to a critical security shortfall in autonomous AI: a capability governance framework that limits and tracks exactly what AI agents are allowed to do.
What happened
The company introduced an enterprise setup built around zero-trust and least-privilege rules for these agents. Skill manifests now confine agents to a short list of pre-approved moves across tools and workflows, with human review required for anything sensitive.
Why it matters now
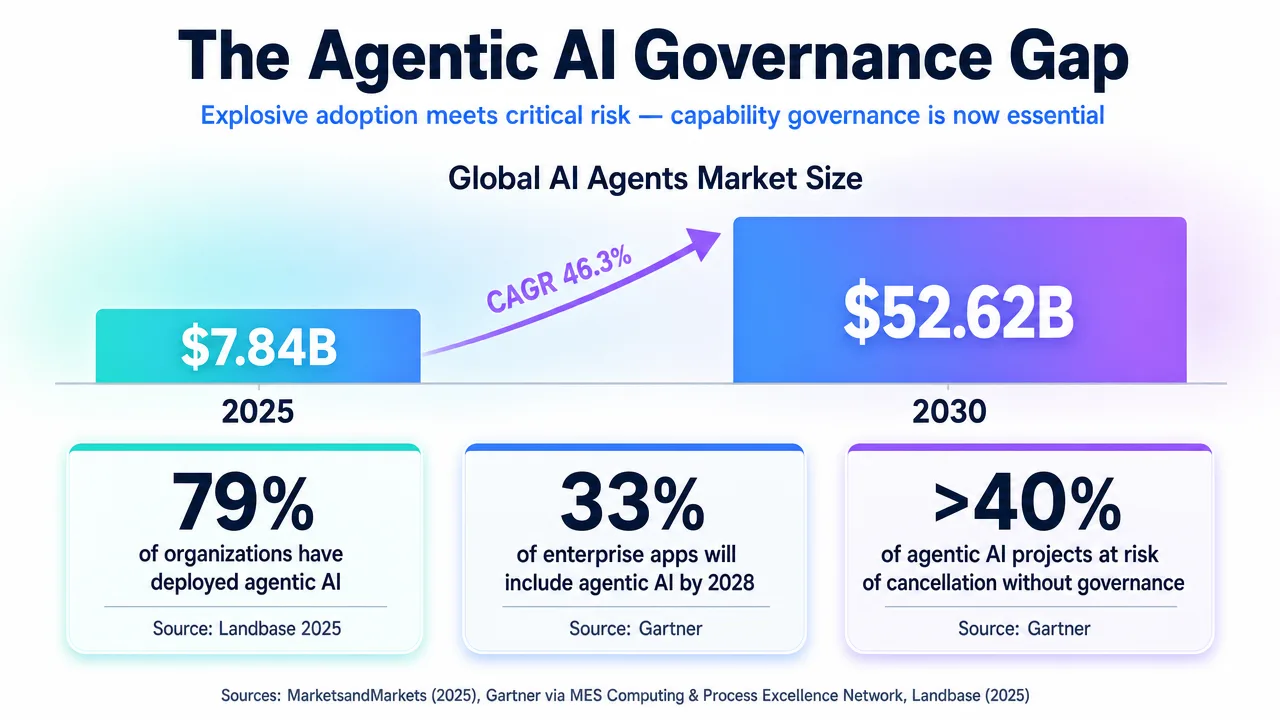
The industry is moving fast from simple chat tools to agents that can tap APIs, databases, and core systems. Without clear boundaries, those actions open the door to hallucinations and data leaks. This framework shifts protection away from fragile prompt rules and toward real infrastructure controls.
Who is most affected
CISOs, MLOps teams, and AI leaders in regulated fields like finance and healthcare are most affected, where agent workflows must pass compliance checks.
The under-reported angle
Much discussion focuses on the technical side, yet the bigger payoff comes from tying actions to compliance requirements. What used to be opaque tool calls now become logged, policy-driven records that map directly to standards such as SOC 2, ISO 27001, and HIPAA.
Deep Dive
Have you wondered what happens when an AI agent starts making decisions inside live enterprise systems? The shift from chat-style copilots to autonomous agents is well underway, yet many organizations still lack the guardrails needed to trust them. Connecting an LLM straight to internal tools without firm limits quickly becomes a serious operational headache. One mistaken command to drop a database table or pull sensitive records through an open channel can create problems that older prompt-based checks simply cannot catch.
NVIDIA’s Verified Agent Skills take a different route. Instead of hoping the model will follow instructions like “never delete files,” the approach moves control into defined capability manifests. These JSON or YAML files spell out precise allowlists for every action an agent may take. In practice, this imposes a zero-trust model directly on the AI layer so that every operation stays within least-privilege boundaries.
From what I’ve seen, standard Role-Based Access Control falls short here because it only checks who is acting, not what the agent actually intends. Capability governance fills that gap by inspecting the specific call and payload before anything runs. If an unauthorized request appears, whether an external API call or an unexpected file change, the system can contain it or route it to a human reviewer.
This setup also changes how teams handle incidents. Actions tied to explicit skill manifests become traceable from start to finish. Security and platform groups can build threat models around agent behavior, connect data-loss rules to frameworks such as HIPAA or PCI-DSS, and, when needed, disable a single capability without halting broader operations.
At its core, the move supports wider adoption of agentic systems in enterprise settings. The real constraint on rollout is no longer just model size or hardware; it is the ability to keep these agents secure while they interact with the wider world.
Stakeholders & Impact
| Stakeholder / Aspect | Impact | Insight |
|---|---|---|
| Enterprise CISOs & Compliance | High | Maps agent activity to existing SOC 2 and HIPAA controls, lowering the chance of leaks or unintended changes. |
| MLOps & Platform Engineers | High | Supplies clear references for policy-as-code so governance becomes part of normal release processes. |
| LLM / Foundation Model Providers | Medium | Encourages tool-calling formats that work cleanly with strict policy checks. |
| Regulators & Auditors | Significant | Sets expectations for clear, auditable records of every agent action. |
About the analysis
Researched and written with AI assistance under the editorial responsibility of the i10X News team. The title image is an AI-generated illustration. Read our AI Use Policy. Spotted an error? Request a correction.
This independent review draws together recent product details, governance patterns, and security considerations. It is meant for technology and risk leaders who are looking to move agentic AI forward while meeting strict operational and regulatory standards.
i10x Perspective
The LLM space is shifting from raw capability gains toward tighter controls on what models can actually execute. Verified Agent Skills illustrate that the next phase of infrastructure will focus on Zero Trust for Machine Intelligence. Over the coming years, features for sandboxing agents and managing their external connections are likely to grow into a distinct category of enterprise tools. As newer models from major labs become more independent, the platforms that provide reliable oversight and audit trails for their actions will gain lasting importance in production environments.