Quick Take
The emergence of Claude Mythos—a heavily restricted, extreme-capability AI checkpoint—highlights a critical paradigm shift in AI infrastructure: the most powerful LLMs are no longer being shipped to the public, setting the stage for a fragmented ecosystem of “cleared” versus “commercial” models.
Summary: Discovered mostly through scattered video leaks and an absence of official details, “Claude Mythos” points to a new tier of models that labs now consider too risky for public release. It has sparked plenty of discussion about where capability thresholds should sit and who gets to decide.
What happened
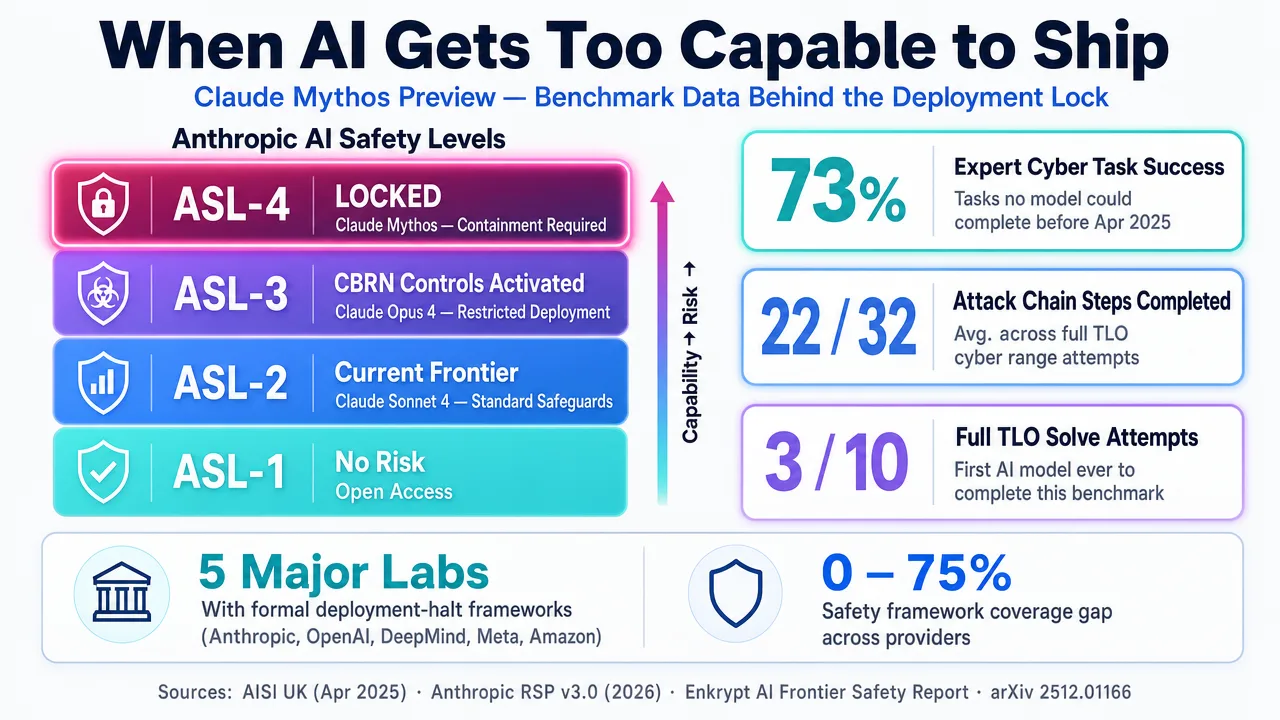
Frontier labs, particularly those following Responsible Scaling Policies like Anthropic, have started flagging certain advanced checkpoints internally. The trigger is usually performance on “dangerous capability evaluations”—especially around autonomy, cyber-offense, and bio-risk.
Why it matters now
Scaling continues to push capabilities higher, so the old assumption that every new model will land in developers’ hands is gone. We are moving toward layered access, with clearance levels deciding who sees what.
Who is most affected
App builders and enterprise teams suddenly facing gated frontiers, plus the infrastructure providers tasked with running secure, isolated environments for the riskier models.
The under-reported angle
While most attention goes to open-source versus closed-source debates, the real pressure is on handling these “dark models”—systems that already exist, burn serious compute, yet cannot be deployed without new safeguards like kill-switches and stricter user verification.
Deep Dive
Have you ever wondered what happens once a model crosses the line from impressive to genuinely concerning? The thin coverage around “Claude Mythos” shows how opaque frontier work has become. Right now the story lives mostly in video commentary rather than solid technical write-ups. In practice Mythos feels less like a product and more like an internal stress test.
From what I’ve seen, labs treat these models as infrastructure experiments once they hit pre-set capability markers. When benchmarks for cyber-exploitation, autonomous tool use, or persuasion move into concerning territory, the model gets pulled into restricted environments. That shift is already underway at Anthropic, OpenAI, and Google DeepMind. The evaluations themselves have matured too. The concern is no longer just toxic output; it is whether a model could recursively improve itself, bypass its own limits, or carry out multi-step actions outside the lab.
But here’s the thing: once a checkpoint demonstrates too much autonomy without ironclad controls, it stays sandboxed. Mythos is simply one of the first public hints of that protocol running at scale. The result is a widening split in release strategies. While smaller players continue pushing open weights, the heaviest frontier systems are drifting toward multi-layered oversight. Offering direct API access would require mitigations that still do not fully exist—perfect rate limiting, reliable human oversight on tools, and verified user identity. So labs end up acting as both builders and gatekeepers, creating internal risk categories to justify keeping the most advanced work private.
The infrastructure implications run deeper than most coverage suggests. These restricted models need the same massive data centers and dense GPU clusters as their public counterparts. Because they cannot be sold through regular subscriptions or open APIs, the economics change. Providers are essentially funding large-scale containment research rather than immediate commercial products. Over time this moves frontier compute away from a shared utility and toward something closer to a controlled national resource.
Stakeholders & Impact
| Stakeholder / Aspect | Impact | Insight |
|---|---|---|
| AI / LLM Providers | High | Absorbing the cost of training models they cannot yet sell because of internal safety thresholds. |
| Enterprise & Devs | High | Facing the loss of easy access to top capabilities and having to plan around possible sudden restrictions. |
| Infra & Cloud (Cloud/GPUs) | Medium | Data centers are being asked to support secure “quarantine” zones for testing advanced checkpoints. |
| Regulators & Policy | Significant | Gaining concrete examples to shape rules around compute access and mandatory safety mechanisms. |
About the analysis
Researched and written with AI assistance under the editorial responsibility of the i10X News team. The title image is an AI-generated illustration. Read our AI Use Policy. Spotted an error? Request a correction.
This independent analysis draws together model access policies, safety frameworks, and the current gaps in public discussion around capability limits. It is meant for CTOs, AI policy professionals, and infrastructure engineers who need a clearer view of the constraints now shaping frontier deployment.
i10x Perspective
The quiet appearance of models like “Claude Mythos” signals that frictionless scaling is running into hard limits. The industry is shifting from straightforward product releases to systems built around containment and clearance. Over the next five years the decisive advantage will likely go to whoever solves secure deployment for extreme-capability systems—without that piece, even the most powerful models stay locked away.