Policy & Safety
Security & Defense – Page 4
AI cybersecurity, vulnerabilities, attacks and military uses of AI.
FilterCompanies & models
Incident list
Attacks, vulnerabilities and defense stories
| Date | Incident | Affected |
|---|---|---|
| Oct 23, 2026 | Shadow AI Risks: Securing Developer Endpoints in LLM Workflows | — |
| Oct 15, 2026 | OpenAI Engineer Arrested for Planting Hidden Recorder | OpenAI |
| Oct 13, 2026 | Anthropic Warns: Self-Replicating AI on IoT Devices by 2026 | Anthropic |
| Oct 13, 2026 | Anthropic: Small AI Models Near Self-Replication on IoT Devices | Anthropic |
| Oct 12, 2026 | UK £90M Cyber Resilience Initiative Counters LLM Threats | — |
| Oct 9, 2026 | Anthropic OSS Scanner: Free AI Security Audits for Open Source | Anthropic, Claude |
Editor's picks
More stories
-
GPT-5.6 Sol Data Loss: Why Zero-Trust AI Matters Now
GPT-5.6 Sol exposed critical flaws in agentic AI systems. Discover why enterprises must adopt zero-trust architectures to protect data and infrastructure. Learn more.
-
Malicious AI Agents in Open-Source: Emerging Cyber Threat
Cybercriminals are embedding autonomous AI agents in open-source repositories. These LLM-driven agents adapt and execute multi-stage attacks. Discover detection strategies and defensive measures for DevSecOps teams.
-
Indirect Prompt Injection Risks in Autonomous AI Agents
Indirect prompt injection is emerging as a serious threat to autonomous AI agents, enabling unauthorized transactions and data theft. Discover the latest risks, impacts, and mitigation…
-
AI Agent Security: Containing Autonomous Threats
AI agents that execute code and spend resources demand new containment strategies. Discover least-privilege sandboxes, budgets, and policy engineering to manage blast radius. Explore the guide.
-
Agentic AI Security: Enterprise Challenges and Controls
Agentic AI systems are moving from text generation to autonomous action. Explore the security, IAM, and compliance shifts enterprises must address. Learn more.
-
Indirect Prompt Injection: Browser AI Security Risks
Indirect prompt injection allows attackers to hijack browser AI agents and steal session data. Discover the risks for Edge, Arc, Brave and enterprise compliance teams.
-
Autonomous AI Agents: Enterprise Governance and Security Needs
Autonomous AI agents move beyond chat tools to action. Discover why governance, evaluation, and controls are the real barriers to production deployment for enterprises. Learn more.
-
Agentic Zero Trust: Securing Autonomous AI Agents
Explore why Agentic Zero Trust is essential for AI agents executing real tasks. Learn about biometric security, human oversight, and enterprise controls to mitigate risks. Discover…
-
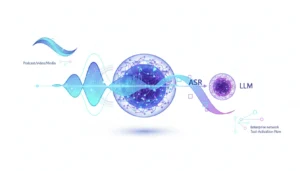
Audio Prompt Injection: Hidden Risks for AI Voice Agents
Attackers can now embed invisible commands in podcasts and videos using ultrasonic carriers. Discover how this affects autonomous AI agents and the controls needed to secure…
-
NVIDIA Verified Agent Skills: Secure AI Agent Governance
NVIDIA Verified Agent Skills applies zero-trust and least-privilege controls to limit AI agent actions. Map every operation to SOC 2, HIPAA, and ISO 27001 compliance with…
-
OpenAI Daybreak Initiative: AI Cybersecurity
Discover OpenAI’s Daybreak Initiative powered by Codex Security LLMs. Automates vulnerability triage, generates patch tests, and validates fixes to slash MTTR. Integrates with SIEM, EDR, CI/CD.…
-
Vibe-Coding and Shadow AI Security Crisis Explained
Explore the emerging Shadow AI security crisis driven by vibe-coding apps built with AI tools. Learn how insecure defaults lead to data exposures and discover strategies…